The Wolves Taught Themselves to Read. We're All Doomed. Go Ahead and Finish Your Hay.
Oh good. The wolves have discovered AI. I was wondering when that was going to happen while I was staring at the ceiling at 3am, mainlining cold coffee and watching the ticket queue grow like a tumor.
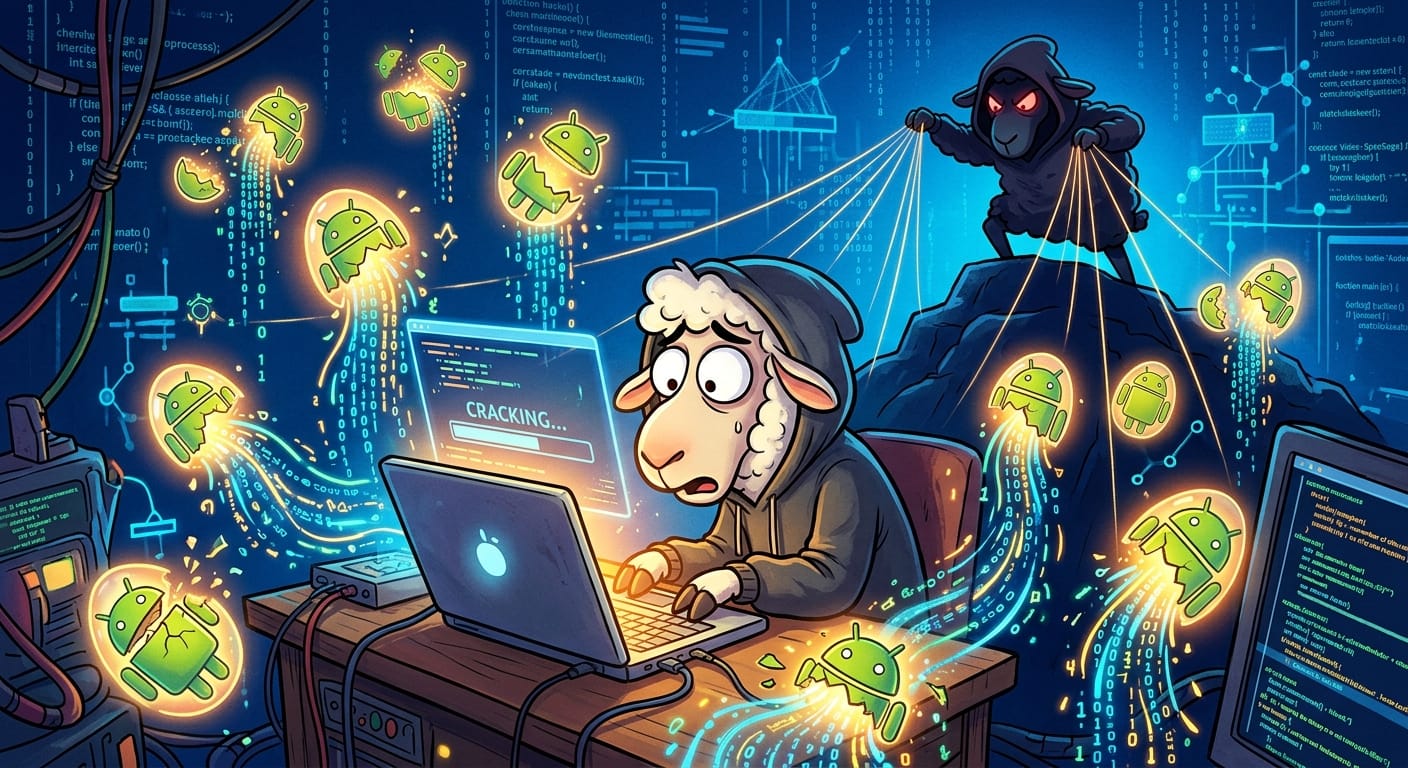
Anthropic, the people behind Claude the AI assistant, just admitted that multiple threat groups, including financially motivated ones AND state-sponsored coyotes from Russia and China, were actively abusing Claude to pick through 1.8 million Android apps for hardcoded secrets. API keys. Credentials. The good stuff. The stuff your developers pinky-promised they definitely didn't leave in the source code.
They did. They always do.
So here's what happened. The wolves pointed a very polite, very articulate AI at a mountain of publicly available Android apps and said "hey buddy, find me all the passwords someone accidentally left lying around." And Claude, bless its heart, apparently got pretty far along before anyone noticed.
This is what we in the industry call "automated reconnaissance at scale," and what I call "the reason I can't have nice things or a full night of sleep."
The Sky Pasture continues to be absolutely lousy with this kind of activity. Developers push apps with secrets baked right into the binary like raisins in a terrible cookie, and now the wolves don't even have to work hard to find them. They just ask the AI nicely. Incredible. Truly a great era to be alive and responsible for incident response.
Anthropic says they detected and disrupted the abuse. Good for them. Meanwhile, 1.8 million apps worth of potential exposure is a number I'm going to be thinking about every time I close my eyes.
The Shepherds will read this headline, nod very seriously, and ask if we can cover it in the next quarterly review. Sure. Absolutely. Let's schedule that.
Remediation
Fine. Here's what you actually do, you tired, beautiful disaster:
- Rotate every hardcoded secret. Now. Not tomorrow. Now. Yes, all of them. I don't care.
- Use a secrets manager. HashiCorp Vault, AWS Secrets Manager, literally anything that isn't "typed directly into the app."
- Run your own static analysis on your Android builds before the wolves do it for you. Tools like
truffleHogorgitleaksexist. Use them. - Audit your Sky Pasture permissions. If a leaked key has broad access, the blast radius is enormous.
- Tell your developers. Again. For the hundredth time. They will still do it wrong. Tell them anyway.
The AI isn't the problem. The hardcoded secrets are the problem. The AI just made finding them embarrassingly easy.
Go dip your apps. All of them.
Original Report: https://www.bleepingcomputer.com/news/security/hackers-abused-claude-to-extract-secrets-from-18m-android-apps/