300 Sheep Tunnels Compromised: The Wolves Were Waiting at the Other End
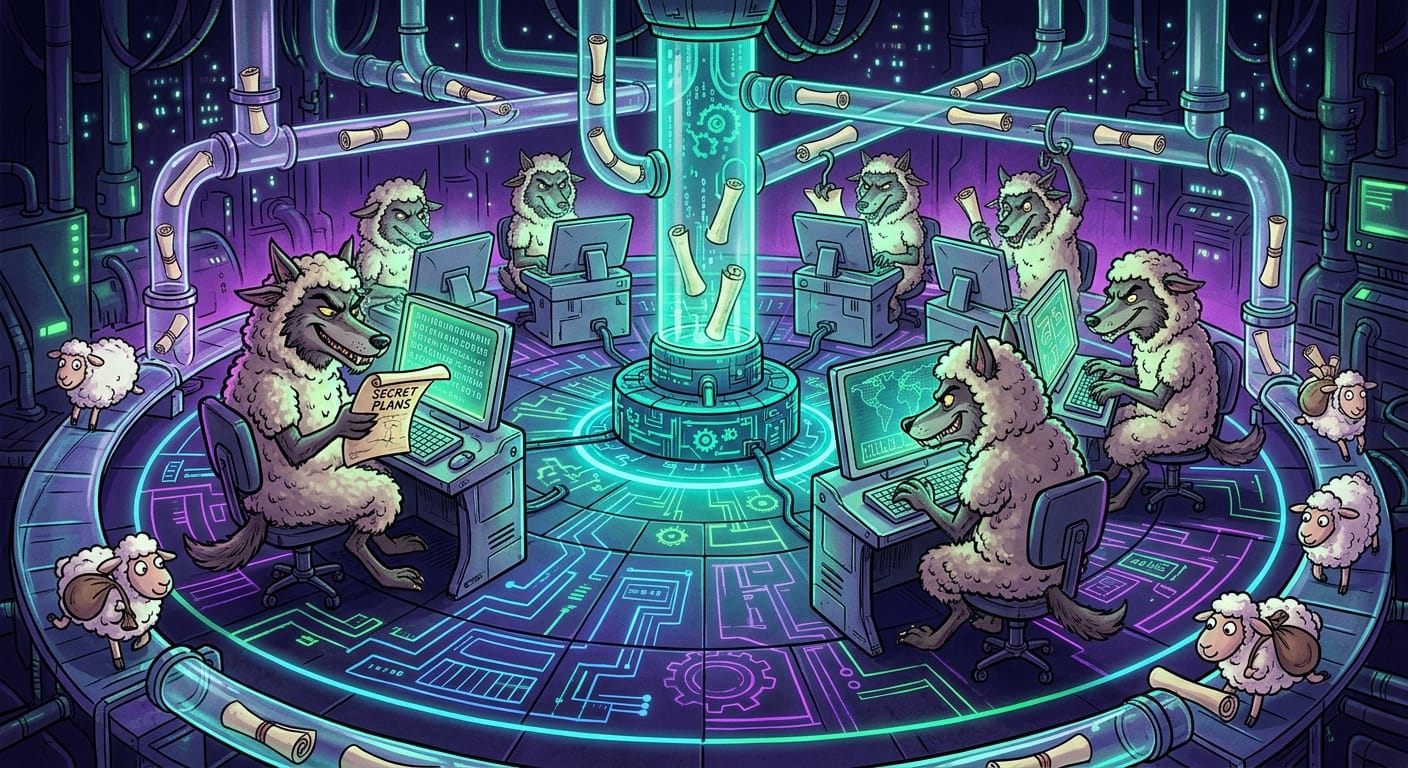
I want you to sit with that number for a moment. Three hundred. Three hundred compromised exit points in what the lambs of the internet call their "anonymous" network. I am not surprised. I told anyone who would listen in 1997 that routing your secrets through infrastructure you do not personally own and physically inspect is not security. It is optimism. And optimism gets you fleeced.
Here is what happened. The wolves seized control of over 300 Tor exit relays during the first five days of October. For those of you who skipped my previous fourteen warnings: the exit relay is where your Sheep Tunnel traffic finally surfaces into the open air. It is the mouth of the tunnel. And someone was standing at the mouth with a net.
Any lamb who logged into an SSH server through Tor during that window, and accepted a suspicious host key prompt without questioning it, handed their password directly to the interception server. Clean. Simple. Elegant, in a way that genuinely depresses me.
This is a classic man-in-the-middle operation. We documented this attack pattern on physical telephone exchanges before most of your current developers were born. The wolf does not need to break down the fence. The wolf simply becomes the last post of the fence. Nobody checks the last post.
The modern obsession with the Sheep Tunnel as a privacy cure-all is, frankly, embarrassing. On magnetic tape, your data went nowhere it was not physically carried. You knew the courier. You had met his mother.
The Shepherds, predictably, have issued no meaningful statement. They are presumably in a meeting about synergy.
Remediation
I will keep this brief because the solutions are not complicated, only ignored.
First. Verify your SSH host keys. Every time. If a server presents a key you do not recognize, you do not click accept and move on with your morning coffee. You stop. Write the expected fingerprint down. On paper. I still do this.
Second. Use key-based SSH authentication and disable password login entirely. A stolen password from an interception server is worthless if passwords are not accepted. This has been best practice since before the Sheep Tunnel existed.
Third. Do not treat the Sheep Tunnel as a complete security solution. It anonymizes your path. It does not sanitize your destination or vouch for the integrity of every relay. The tunnel has an exit. Always ask who built it.
Fourth. Run your own relay infrastructure if you depend on this network professionally. Yes, it is more work. That is the point. Security was never supposed to be convenient.
Stay paranoid, check your keys, and for the love of all that is holy, stop clicking accept on unrecognized fingerprints.
Original Report: https://thehackernews.com/2026/10/attackers-hijacked-over-300-tor-exit.html