ShinyHunters Claims They Sheared The Entire FBI Flock
I have seen a great many things in my career. I have watched magnetic tape reels spin through the night, transferring data with a dignity and deliberateness that modern systems simply cannot replicate. I have negotiated security protocols over dial-up connections that, frankly, had more integrity than anything running on a containerized microservice today.
But this. This is something else.
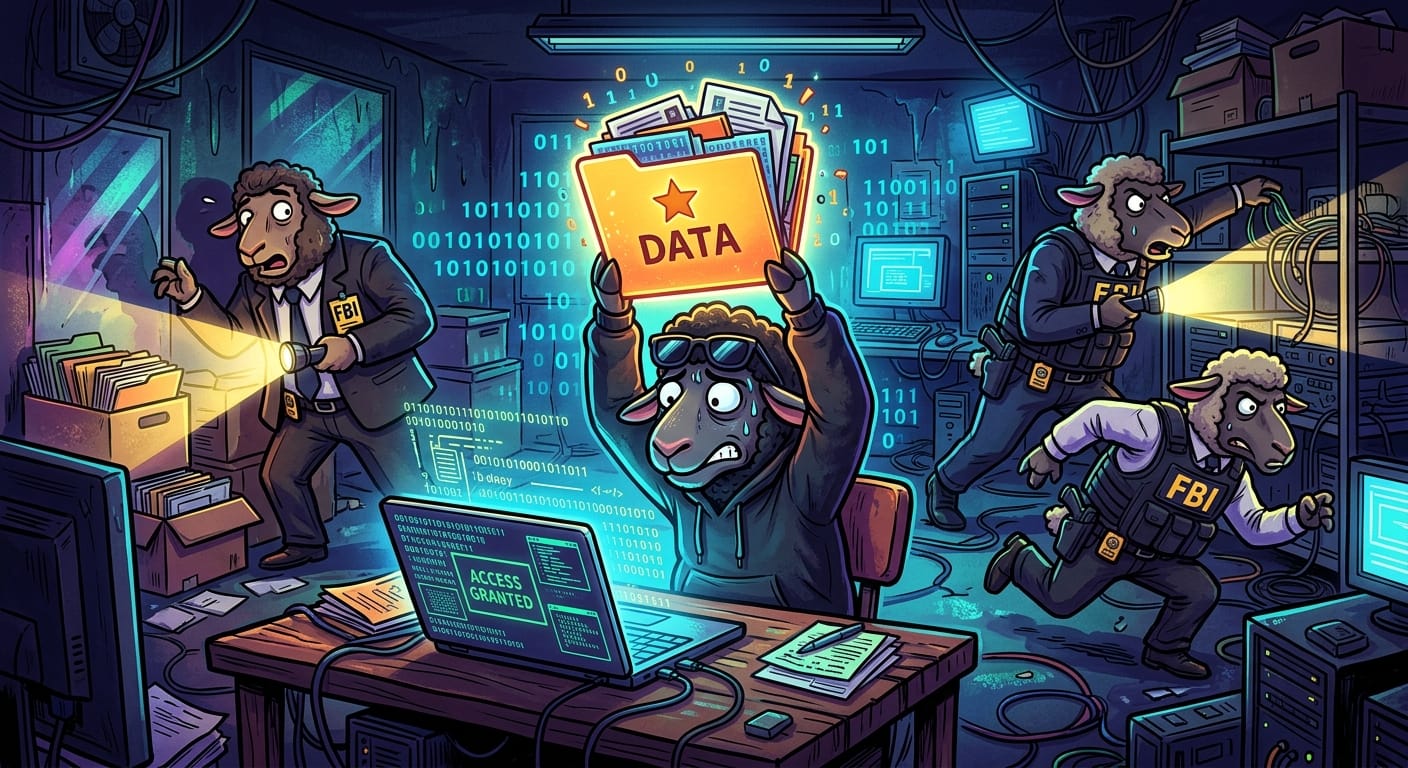
The extortion collective known as ShinyHunters is claiming they walked straight through the Electric Fence at the Federal Bureau of Investigation and made off with sensitive wool on nearly every agent in the building. Current staff. Former staff. Job applicants. The whole flock, sheared clean.
Their statement, posted to the dark web with what I can only describe as theatrical confidence, reads: "We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI."
I want you to sit with that for a moment.
The wolves are not hiding in the tree line anymore. They are standing in the middle of the pasture, holding a microphone.
Now, I will note that ShinyHunters has a well-documented history of making claims that range from completely accurate to wildly embellished. The FBI has not confirmed the breach. This could be a bluff. It could be partial. It could be the real thing.
The problem is, in my experience, the Shepherds at the top never actually know until someone is already selling the wool at market. Management has a remarkable talent for being the last to find out that the fence has a hole in it.
And if the Sky Pasture is involved in any of this data storage, I am going to need to lie down.
The Old Days had their virtues. Air-gapped systems. Physical media. You knew exactly where your data was because you could point at the tape and say, "There. That is the data. It is not floating somewhere over Virginia."
Modern tools are soft. Everyone is comfortable. Nobody is paranoid enough. That is the problem.
Remediation
For those of you still capable of taking direction:
- Audit your access logs. Actually look at them. I know this is considered an extreme sport in 2026, but do it.
- Enforce multi-factor authentication across all entry points. No exceptions for senior Shepherds who find it inconvenient.
- Assume the fence has holes you have not found yet. Conduct penetration testing. Regularly. Not once in 2019.
- Limit data aggregation. If the wolves can grab everything in one visit, you have already failed the architecture review.
- Treat job applicant data like operational data. It is sensitive. Store it accordingly.
Stay paranoid out there, because clearly nobody else is doing it for you.
Original Report: https://thehackernews.com/2026/09/shinyhunters-claims-fbi-breach-says-it.html