Sky Pasture Neighbors Can Apparently Just Read Your Mail Now: CVE-2026-99312
Oh good. Another Tuesday.
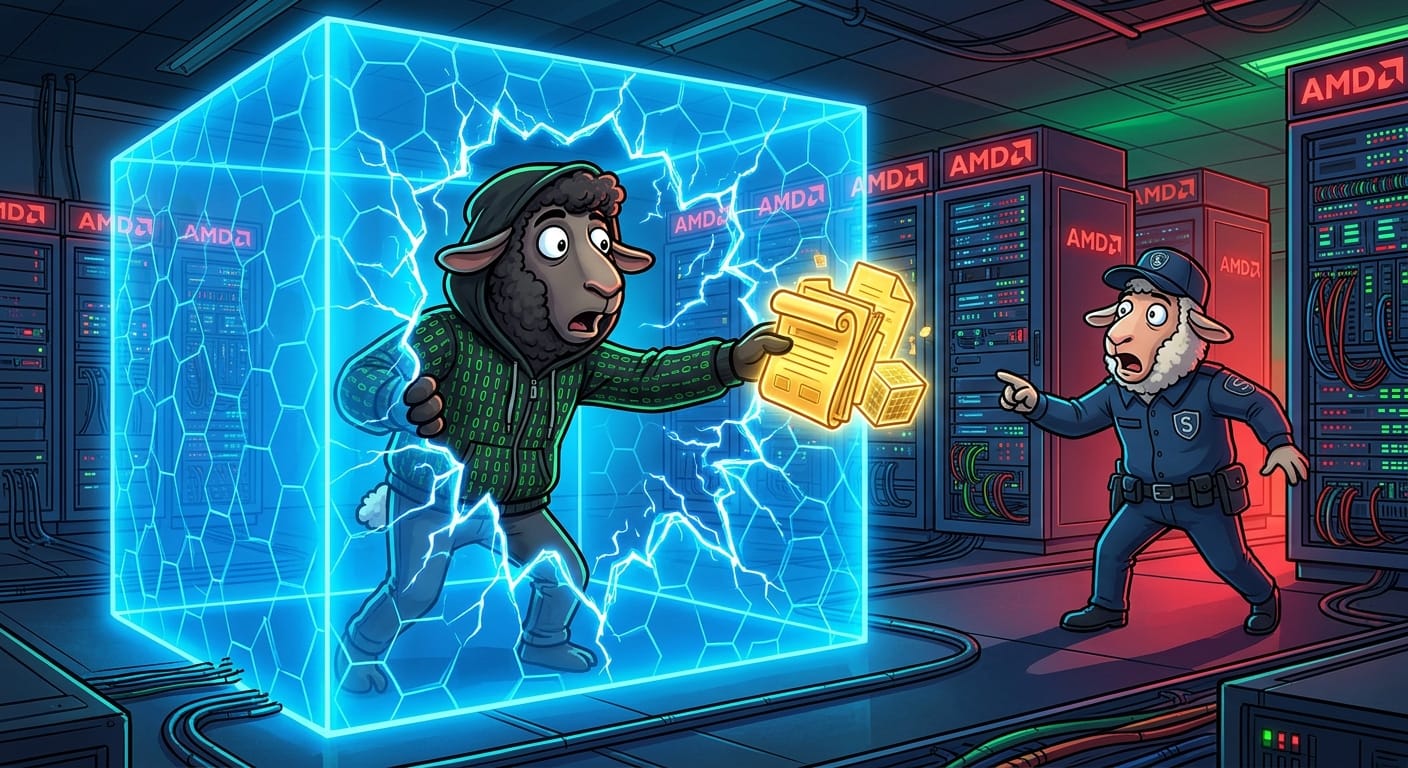
So some researchers, bless their well-rested little hearts, spun up a virtual machine on DigitalOcean and just. Read the host's memory. 127 gigabytes of it. From inside their own rented VM. Like they were borrowing a cup of sugar except the sugar was every other customer's data on that physical box.
The culprit is a hole in the fence inside Linux's KVM hypervisor, specifically on AMD hosts with nested virtualization turned on. CVE-2026-99312. Write it down. Tape it to your monitor. Cry about it later.
Here's the part that makes my left eye twitch: this is a shared Sky Pasture environment. You know what lives in shared host memory? Other VMs. Other customers. Other people's secrets that they trustingly handed to a cloud provider because a Shepherd in a polo shirt told them it was "enterprise-grade secure."
It was not enterprise-grade secure.
The attack doesn't require the Flock to click anything, which is honestly a nice change of pace. No fake grain involved. No "click here to claim your free bale." Just a Wolf with a rental VM and a curious disposition, quietly hoovering up whatever was sitting in memory nearby.
Could be credentials. Could be encryption keys. Could be some other company's entire production database taking a nap in RAM. Who knows. The researchers stopped at 127 GB but the fence post was still wobbly.
The good news, and I use that term loosely because nothing is good, is that fixed kernels have shipped. The bad news is that I now have to figure out which of our AMD hosts have nested virtualization enabled, and I have seventeen open tickets already, and someone just emailed me asking why the printer is slow.
The printer. Is slow.
Remediation
Look, here's what you do, and I say this with the energy of a sheep who has been awake since yesterday:
- Patch your kernel. Fixed versions are out. Apply them. Yes, it requires a reboot. Yes, the Shepherds will complain about the maintenance window. Do it anyway.
- Audit nested virtualization. If you don't explicitly need it enabled on your AMD hosts, turn it off. It is not a feature you are using. It is a feature that is using you.
- Check your cloud provider's status. If you're on a shared AMD-based Sky Pasture environment, ask your provider directly whether they've applied the fix. In writing. With timestamps.
- Assume the worst. If you were running sensitive workloads on unpatched AMD KVM hosts, treat that memory as compromised and rotate anything that might have been in it.
Go patch. I'll be here, staring at the ceiling.
Original Report: https://thehackernews.com/2026/11/new-linux-kvm-flaw-cve-2026-99312-lets.html