The Wolf A/B Tested Its Fleas On 178 Pastures Simultaneously. Congratulations, Modern Web.
I have been saying this for thirty years. Thirty years. You do not hand a stranger the keys to your barn because they promised to optimize your hay arrangement.
And yet. Here we are.
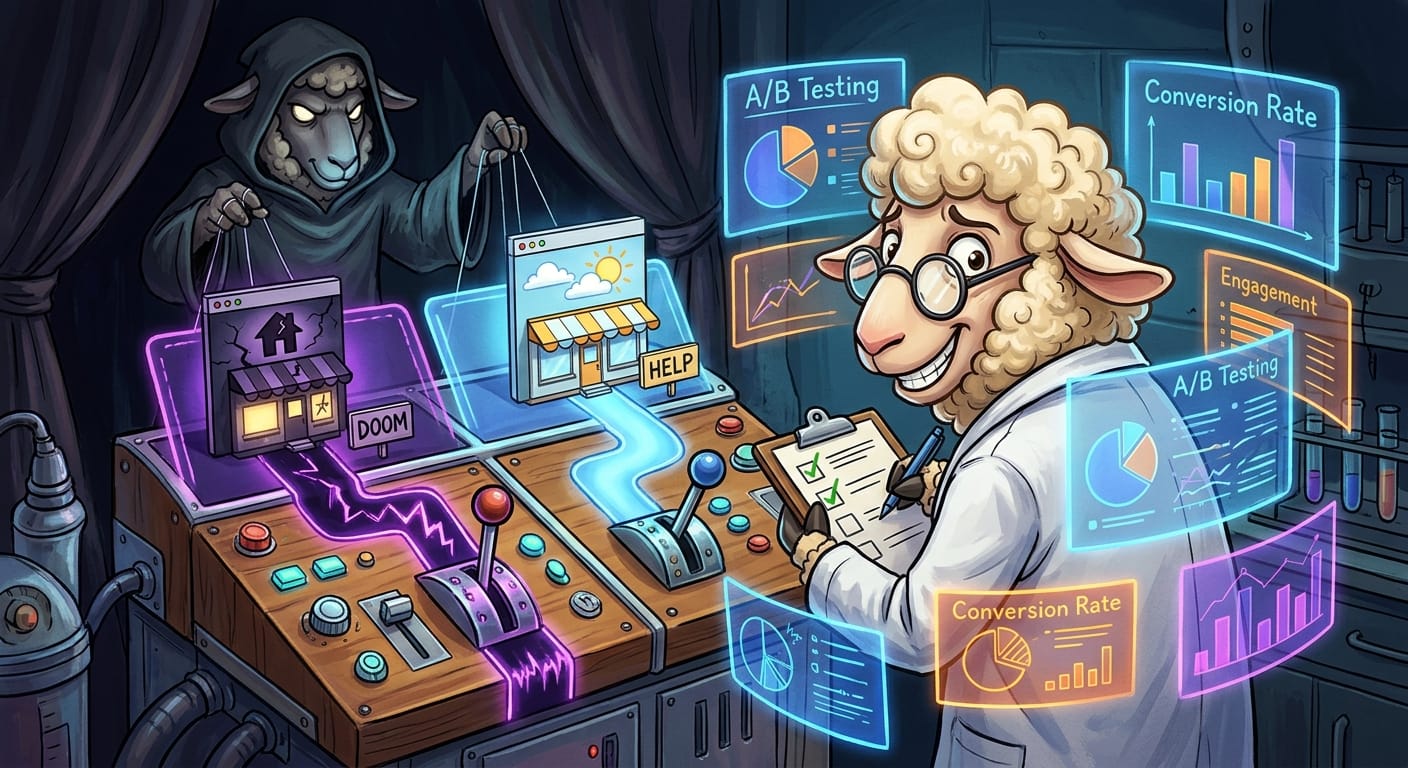
A company called Optimizely, whose entire business model is "let us inject code into your website from our servers," was compromised. The wolves got in, swapped the legitimate scripts for parasites, and proceeded to conduct what I can only describe as a scientifically rigorous infestation study across 178 of the web's most visited pastures. The BBC. CNN. Equifax. Zoom. The flock visiting these sites had data-stealing ticks silently loaded onto their machines. No warning. No opt-out. Just fleas, delivered at enterprise scale.
I want you to sit with that. The attacker used an A/B testing platform to A/B test their own malware deployment. That is, frankly, impressive operational discipline. I am furious, but I am not blind to the craft.
The core failure here is not Optimizely specifically. The failure is that the modern web has decided that third-party scripts are perfectly fine to load from anywhere, at any time, with no verification whatsoever. We call this a Content Security Policy. It exists. It has existed. The shepherds at these major organizations apparently decided it was optional.
In the old days, you ran your own code on your own iron. You knew every byte on that magnetic tape because you put it there. There was no "sky pasture" from which mysterious optimization scripts could descend uninvited. You controlled the perimeter. The electric fence was yours.
Now we have 178 elite organizations discovering that their entire front door was, in practice, managed by a third party they trusted implicitly and monitored not at all. Equifax is on this list. Equifax. I will not elaborate further. My blood pressure has limits.
Remediation
Right. Here is what you do, and I should not have to tell you this in the year 2026.
Implement a strict Content Security Policy. Whitelist the specific sources allowed to execute scripts on your domain. Everything else gets blocked at the electric fence. This is not optional, it is foundational.
Audit your third-party dependencies. Every script tag you load from an external domain is a hole in the fence you do not own. Catalog them. Question each one. Ask yourself if you truly need seventeen marketing pixels and an "experience optimization" platform with write access to your users.
Subresource Integrity checks. Hash your third-party scripts. If the file changes without your knowledge, the browser refuses to run it. This technology has been available since 2016. Use it.
The lambs deserved better. They always do.
Stay paranoid, the wolves certainly are.
Original Report: https://krebsonsecurity.com/2026/11/attackers-used-optimizely-to-a-b-test-malware-on-top-websites/