Someone Stuffed a Snitch Board Inside Your Hardware Wallet and Honestly I'm Not Even Surprised
Oh good. A hardware wallet with a bonus feature nobody asked for. An extra circuit board, quietly texting your recovery phrase to some wolf over a mobile network. Like a little parasite with a SIM card. I need more coffee.
Here's what happened, since apparently I have to explain this instead of sleeping.
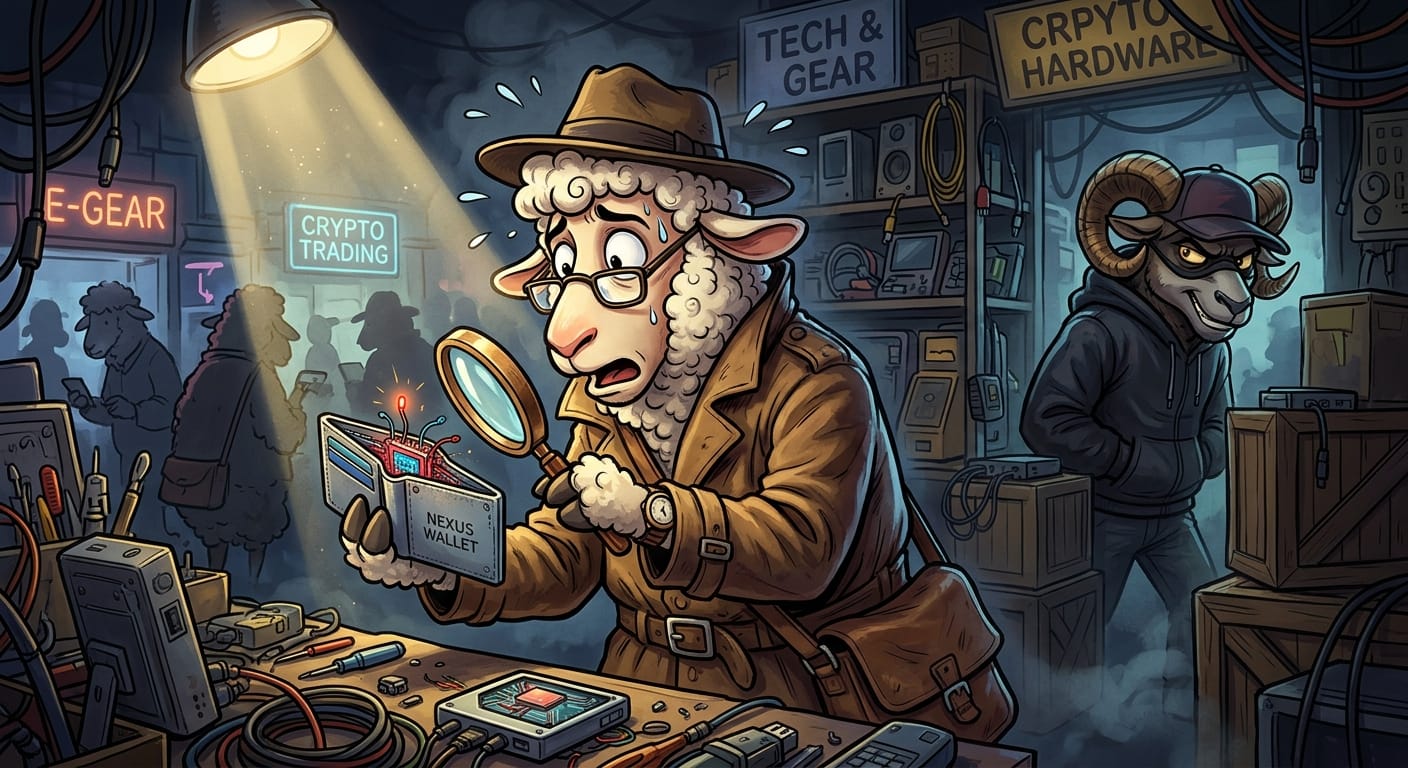
A lamb bought a Trezor Safe 5 from a reseller called CryptoBilis. Cute name. Very trustworthy. The device had a hidden circuit board crammed inside it, and that board was cheerfully broadcasting the wallet's recovery phrase over a cellular connection. To whom? To whoever put it there. Which was not Trezor.
This is a supply chain attack. A physical one. The wolf didn't need to phish anyone. The flock didn't need to click anything. The device itself was compromised before it ever touched a single hoof. Which, fine, is technically impressive. Still infuriating.
Trezor hasn't physically examined the device yet as of this writing, which is a sentence I hate typing. They're working on it. I assume.
What they HAVE done is told every lamb who bought a Trezor from CryptoBilis since March 2026 to move their funds immediately and generate a fresh recovery phrase on a clean, verified device. That's the right call. That's the only call.
The Shepherds in your organization who told you that buying crypto hardware from a random third-party reseller was "probably fine" owe you an apology. They will not deliver it. I know this from experience.
The Sky Pasture does not protect you from a compromised device that was tampered with before you even opened the box. Nothing does, except buying directly from the manufacturer and verifying the packaging integrity like your financial life depends on it. Because it does.
Remediation
Look, here's what you do and I'm only saying it once because I'm exhausted:
- Buy hardware wallets directly from the manufacturer. Not a reseller. Not a marketplace. Not your cousin.
- Check tamper-evident seals before you do anything with the device.
- If you bought from CryptoBilis since March 2026, move your funds NOW. Generate a new recovery phrase on a verified device.
- Never enter a recovery phrase on a device you didn't buy yourself, from a verified source. Ever. I don't care what the Shepherds say.
- Treat your recovery phrase like it's the only thing standing between you and financial ruin. Because it is.
Supply chain attacks are not new. Wolves with soldering irons are not new. The flock being shocked by this is, somehow, eternal.
Go check your wallets, I'll be under my desk.
Original Report: https://thehackernews.com/2026/10/trezor-warns-of-suspected-hardware.html