The Sheep Register Is Open: Any Wolf May Now Sign Itself In As Administrator
I have been in this field since before most of your "DevOps engineers" knew how to spell TCP/IP. I have seen bad. I have seen catastrophic. But this, this particular situation with FreeIPA, represents a category of failure that would have gotten someone escorted from the building in 1994.
Let me be precise about what has happened here.
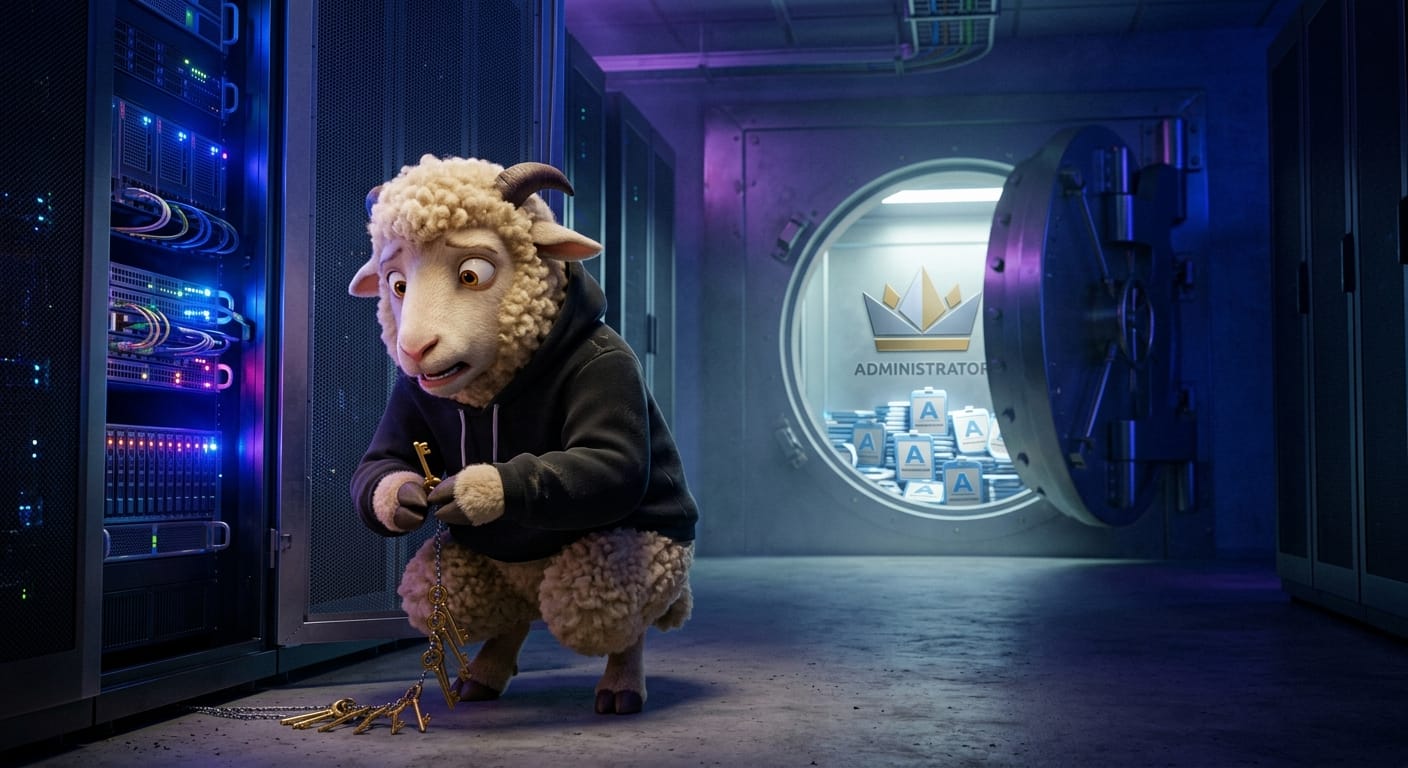
An anonymous client, meaning a member of the flock who has never once presented credentials, never knocked, never introduced itself, can walk up to the directory, invent a Kerberos identity of its own choosing, and place that identity directly into the administrators group. No invitation. No challenge. No friction whatsoever.
In my day, we called that "the wolf writing its own name in the shepherd's ledger." We also called it grounds for immediate termination.
The attack chains two flaws. First, the hole in the fence inside FreeIPA itself. Second, a corresponding weakness in the 389 Directory Server, which handles the LDAP database underneath it all. One flaw enables the approach. The second flaw enables the conquest. Together, they constitute a complete and elegant disaster.
FreeIPA, for those Shepherds currently reading this on their phones during a budget meeting, is your Linux domain's entire identity management infrastructure. It decides who may log in. Everywhere. Across your whole pasture. Compromising it is not a "medium severity" incident. It is a total collapse of the electric fence.
I want to be clear: this is not a sophisticated nation-state technique requiring exotic tooling. This is an anonymous client doing paperwork. The wolves are not even breaking a sweat.
The Sky Pasture crowd will, of course, tell you their managed identity solutions are immune. I am choosing not to engage with that claim today. My blood pressure has limits.
Remediation
Listen carefully, because I will not repeat myself at this volume.
Patch immediately. Red Hat has issued updates for both FreeIPA and 389 Directory Server. Apply the ointment. Both layers. Not one, both.
Audit your administrators group. Right now. Before you finish reading this sentence. If you see any identity in there that your team did not personally and consciously create, you have already been visited.
Restrict LDAP exposure. Anonymous LDAP binds should not be reaching your directory server from arbitrary network positions. This is not new advice. I gave this advice in a different century.
Review Kerberos principal creation logs. Look for anything that smells like a wolf naming itself "admin_definitely_a_real_sheep."
The magnetic tape backups of 1997 never had this problem, because we did not let anonymous strangers touch the tape.
Stay suspicious, and for the love of wool, patch your directories.
Original Report: https://thehackernews.com/2026/09/freeipa-flaw-chain-lets-anonymous.html