The Wolves Poisoned the Water Trough. Briefly. Repeatedly. And Nobody Noticed.
I want you to understand something before I continue. AOMEI Backupper is backup software. Its entire purpose, its singular reason for existing, is to protect data. And someone compromised its update mechanism. The irony is not lost on me. It is, in fact, sitting in my office drinking my coffee.
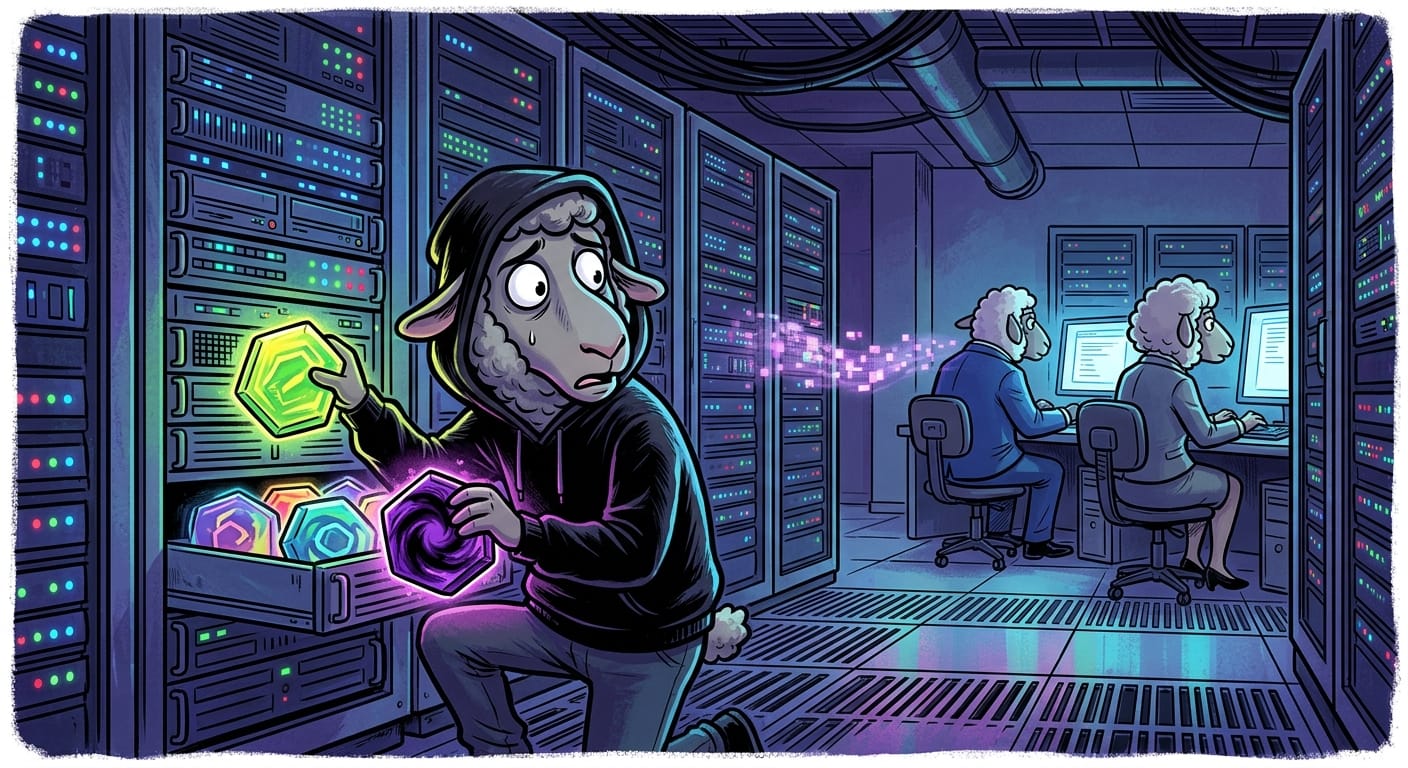
Between May and July of 2026, wolves made repeated, surgical modifications to files sitting on AOMEI's own update servers. Five to ten minutes at a time. In and out. Clean. Professional. The kind of patience I have not seen since certain gentlemen in East Berlin who shall remain nameless.
Any lamb whose copy of Backupper happened to check for updates during one of those windows quietly downloaded and executed a backdoor. No fanfare. No warning. Just a tick, burrowing in, making itself comfortable.
The Sky Pasture crowd will tell you this is a "supply chain attack." I call it what it is: someone found a gap in the fence, slipped through repeatedly over two months, and left a parasite behind each time before anyone looked up from their smartphones.
Google Threat Intelligence Group and Mandiant eventually noticed. Good for them. I noticed the milk was sour, metaphorically speaking, approximately two months after the cows were already compromised. But I digress.
The truly maddening part is the update mechanism itself. In the old days, you verified your binaries against a hash you received separately, over a different channel, ideally written on paper and stored in a filing cabinet. A physical one. With a lock. These modern automated update pipelines are just open troughs sitting in a field. You are trusting that nobody touched the water. Extraordinary.
The Shepherds, naturally, have issued statements. I am sure those statements are very comforting.
Remediation
Do not look at me like that. You already know what I am going to say.
1. Verify your update integrity. Check whether any instance of AOMEI Backupper on your network updated between May and July 2026. If it did, assume the flock is infested and begin incident response immediately.
2. Audit your update pipeline assumptions. If your software trusts its own vendor's server unconditionally, with no secondary signature verification, you have an open trough. Fix it.
3. Monitor for short-window anomalies. Five to ten minutes is below most alerting thresholds. Tune your detection accordingly. The wolves know your blind spots better than you do.
4. Apply available patches. AOMEI has reportedly addressed this. Shear the affected systems, dip them properly, and document everything.
5. Brief the Shepherds. Keep it simple. Use small words. Bring a diagram.
Stay paranoid out there, the wolves certainly are.
Original Report: https://thehackernews.com/2026/10/attackers-tampered-with-aomei.html